How infostealers create corporate risk
Stolen identities, browser sessions and personal-device infections can connect to business systems.
MNSEC 2026 recap
· Ulaanbaatar, Mongolia
Our founder, Yusuf Arslan Polat, spoke in Ulaanbaatar about infostealer-driven corporate access and agentic threat intelligence.
The talk brought together Istary’s work in cybersecurity and AI: turning complex threat data into findings security teams can investigate and act on.
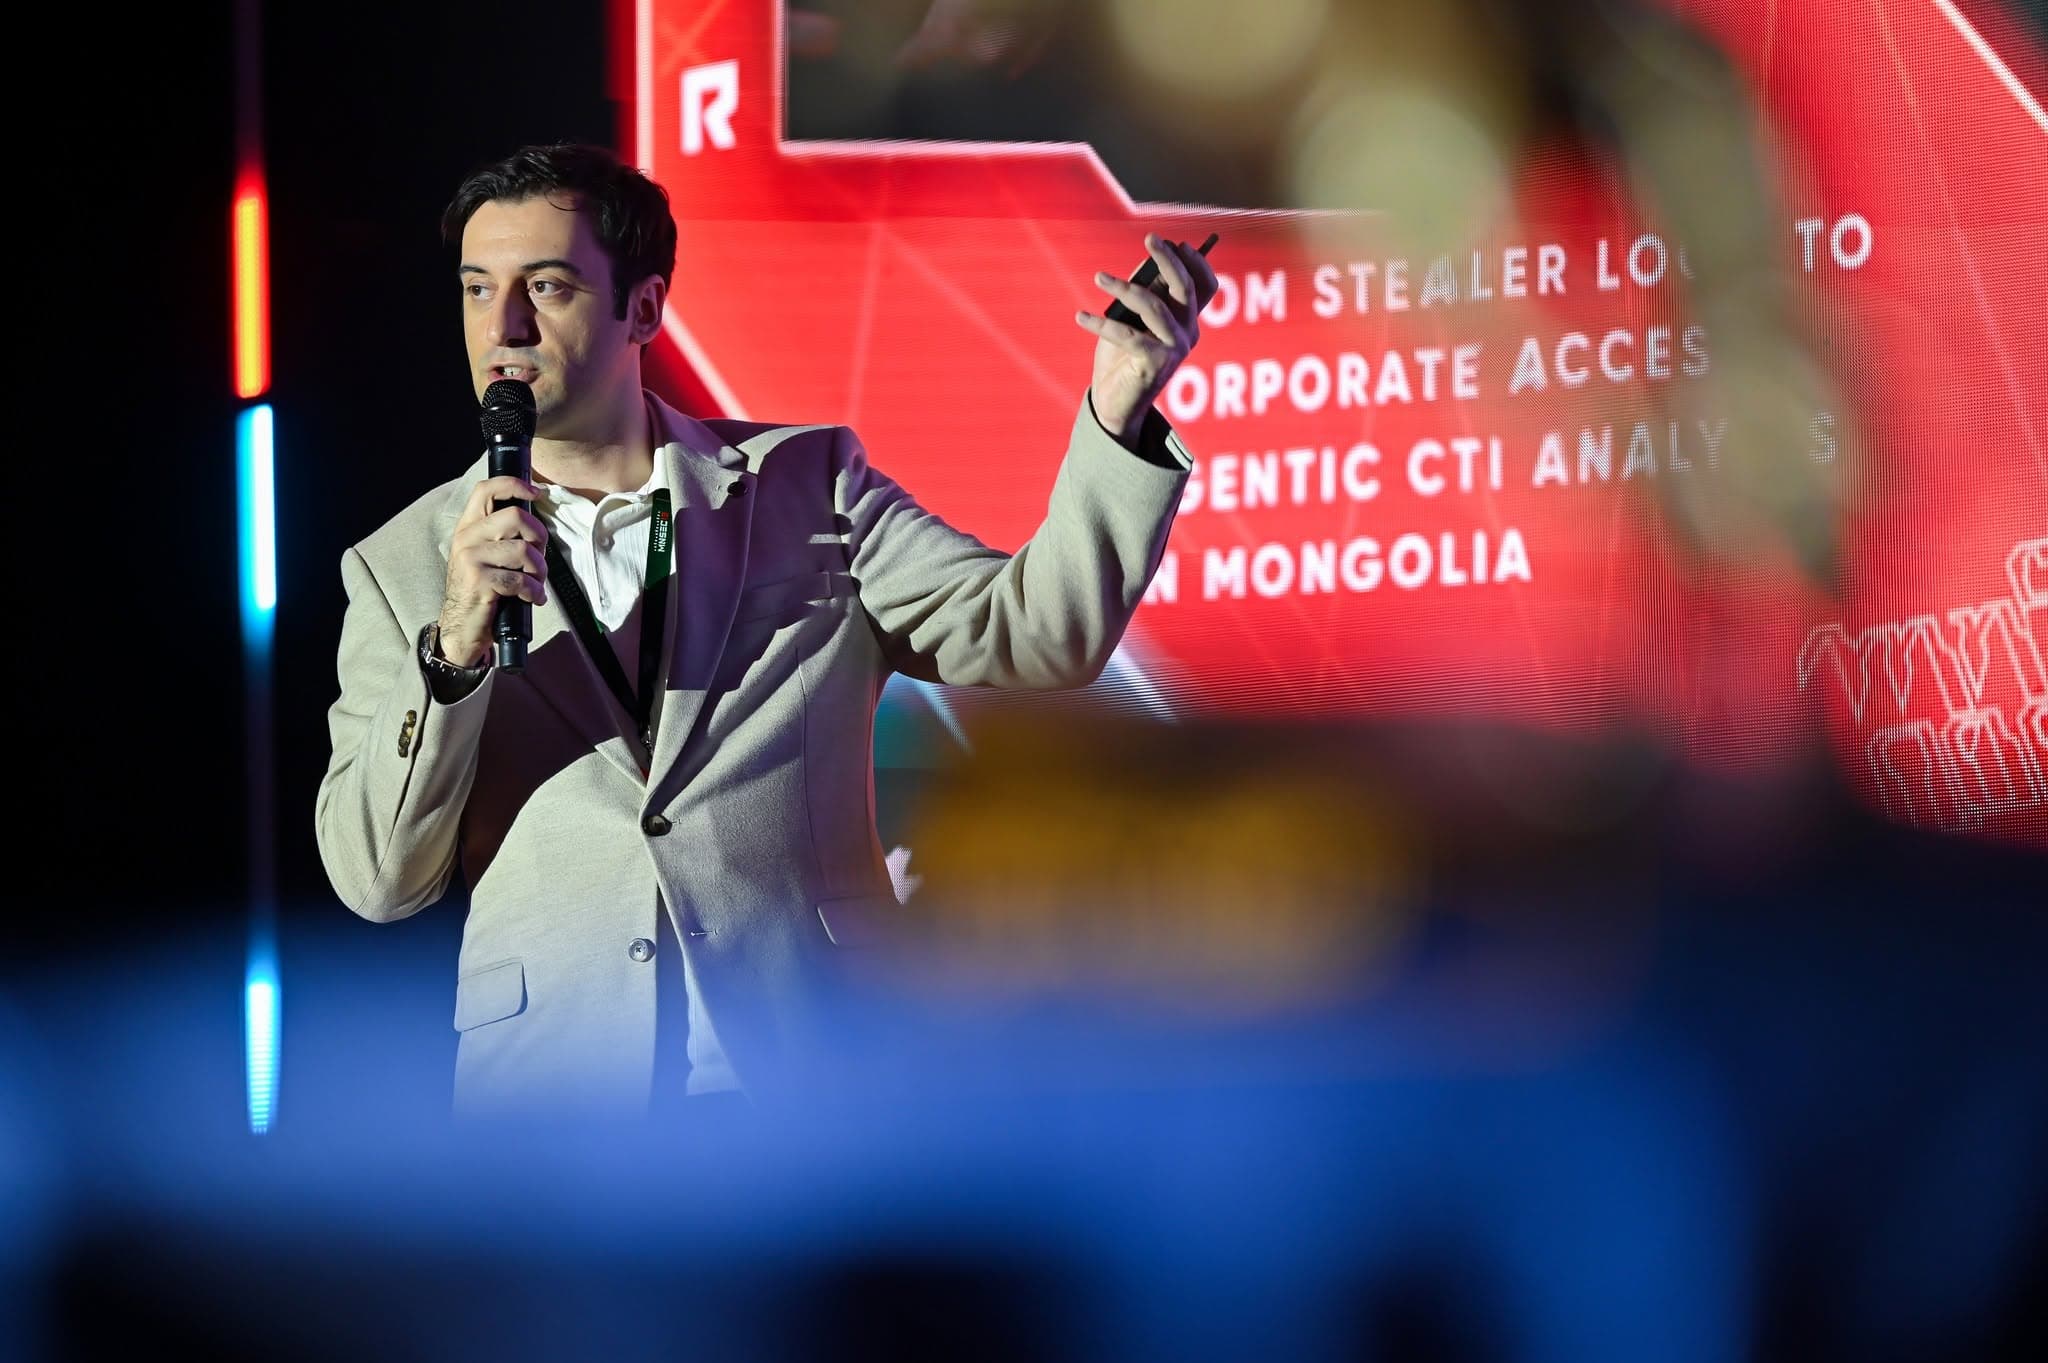
The talk
Using infostealer evidence as a case study, the session explored how AI-assisted investigation can connect identities, devices and business systems, with Mongolia-specific context and analyst review.
Visit the official MNSEC websiteStolen identities, browser sessions and personal-device infections can connect to business systems.
Extracting entities, correlating evidence and prioritizing findings in large, messy threat datasets.
Separating observed evidence from inference, then checking exposure and deciding what to contain.
Continue the conversation
Request a free exposure report for your organization. We’ll review our Mongolia-focused infostealer dataset and send you a redacted report within one business day.
Your report includes
A concise, redacted view of evidence connected to your organization—not a generic count or an unverified breach claim.
Organization-linked identities and devices
Corporate logins and business systems referenced
Recency, malware family and exposure timeline
Priorities for investigation and containment
Contact Istary
Ask about threat intelligence, security testing, incident response, training or technology enablement. Tell us what you need and we’ll follow up directly.